Please enable Javascript to view the contents

Linux 与网络排查笔记合集

 ·  ☕ 6 分钟

Linux 与网络排查笔记合集

本文把若干零散的排查与操作记录合并在一起,每条都是当时环境下的实测结果;环境变化后命令可能失效,以官方文档为准。

如何设置端口仅对指定 IP 开放访问

1. 主机服务端口

1
2
iptables -I INPUT -p tcp --dport 80 -j DROP
iptables -I INPUT -p tcp -s 1.2.3.4 --dport 80 -j ACCEPT

这里仅允许 1.2.3.4 访问本地主机的 80 端口。

2. Docker 服务端口

对于类似 docker run -d -p 80:80 shaowenchen/demo:whoami 运行的服务,上面的方法无效,需要在 DOCKER-USER 链中添加规则。

Docker 会将 iptables 规则添加到 DOCKER 链中,如果需要在 Docker 之前添加规则需要添加到 DOCKER-USER 链中

1
iptables -I DOCKER-USER -i ens192 ! -s 1.2.3.4 -p tcp --dport 80 -j DROP

ens192 是本地的网卡,这里仅允许 1.2.3.4 访问本地主机的 80 端口。

3. 清理环境

1
2
yum install -y iptables-services
systemctl restart iptables.service

如果需要在主机重启之后 iptables 设置,依然有效,需要安装 iptables-services 并保存

1
2
yum install -y iptables-services
service iptables save

4. 参考

安装 CentOS 之后,需要做的几件事

1. 更换镜像源

首先备份官方的源

1
mv /etc/yum.repos.d/CentOS-Base.repo /etc/yum.repos.d/CentOS-Base.repo.backup

下载新的源到 /etc/yum.repos.d/

CentOS 5

1
wget -O /etc/yum.repos.d/CentOS-Base.repo http://mirrors.aliyun.com/repo/Centos-5.repo

CentOS 6

1
wget -O /etc/yum.repos.d/CentOS-Base.repo http://mirrors.aliyun.com/repo/Centos-6.repo

CentOS 7

1
wget -O /etc/yum.repos.d/CentOS-Base.repo http://mirrors.aliyun.com/repo/Centos-7.repo

生成元数据缓存

1
yum makecache

2. 访问 NTFS 文件系统

Linux 内核目前只支持对微软 NTFS 文件系统的读取。 ntfs-3g 是微软 NTFS 文件系统的一个开源实现,同时支持读和写。

ntfs-3g 在 epel-release 源中,执行命令查找 epel 源:

1
yum search epel

安装 epel-release 源:

1
yum install epel-release.noarch

安装 ntfs-3g,执行命令:

1
yum install ntfs-3g

3. 修复 Grub 引导 Windows

由于Linux系统不能识别 Windows 操作系统的分区,所以还得先安装 ntfs-3g。

恢复 grub 配置文件,只需要一条命令:

1
grub2-mkconfig -o  /boot/grub2/grub.cfg

4. 安装 Google Chrome

添加源

1
2
3
4
5
6
7
8
cat << EOF > /etc/yum.repos.d/google-chrome.repo
[google-chrome]
name=google-chrome
baseurl=http://dl.google.com/linux/chrome/rpm/stable/x86_64
enabled=1
gpgcheck=1
gpgkey=https://dl.google.com/linux/linux_signing_key.pub
EOF

安装可以选稳定版、测试版:

1
yum install google-chrome-stable

或

1
yum install google-chrome-beta

5. 安装 VS Code

添加源

1
2
rpm --import https://packages.microsoft.com/keys/microsoft.asc
sh -c 'echo -e "[code]\nname=Visual Studio Code\nbaseurl=https://packages.microsoft.com/yumrepos/vscode\nenabled=1\ngpgcheck=1\ngpgkey=https://packages.microsoft.com/keys/microsoft.asc" > /etc/yum.repos.d/vscode.repo'

安装:

yum install code

CentOS 7 安装 Java 开发环境

1. 编译报错:java.nio.file.NoSuchFileException

在编译 Jenkins 插件时,提示错误信息如下:

1
2
3
4
mvn package

Compilation failure
[ERROR] java.nio.file.NoSuchFileException: /root/java/target/classes/META-INF/annotations/hudson.Extension

原来 Maven 使用的是 JAVA_HOME 而不是 PATH,找不到 Java 运行环境导致,而且 Java 11 不行,Java 1.8 才能正常编译。

2. 安装 JDK

  • 安装 Java 11
1
yum install -y java-11-openjdk-devel
  • 安装 Java 1.8
1
yum install -y java-1.8.0-openjdk-devel

3. 选择 JDK 版本

选择当前 JDK 版本:

1
2
3
4
5
6
7
8
alternatives --config java

There are 2 programs which provide 'java'.

  Selection    Command
-----------------------------------------------
   1           java-11-openjdk.x86_64 (/usr/lib/jvm/java-11-openjdk-11.0.7.10-4.el7_8.x86_64/bin/java)
*+ 2           java-1.8.0-openjdk.x86_64 (/usr/lib/jvm/java-1.8.0-openjdk-1.8.0.252.b09-2.el7_8.x86_64/jre/bin/java)

选择 2 之后, /usr/lib/jvm/java-openjdk 即为当前选择的版本。

 1
 2
 3
 4
 5
 6
 7
 8
 9
10
11
12
ls -l /usr/lib/jvm

lrwxrwxrwx 1 root root   26 Jul  1 15:42 java -> /etc/alternatives/java_sdk
lrwxrwxrwx 1 root root   29 Jul  1 15:42 java-11 -> /etc/alternatives/java_sdk_11
lrwxrwxrwx 1 root root   37 Jul  1 15:42 java-11-openjdk -> /etc/alternatives/java_sdk_11_openjdk
drwxr-xr-x 8 root root 4096 Jul  1 15:42 java-11-openjdk-11.0.7.10-4.el7_8.x86_64
lrwxrwxrwx 1 root root   34 Jul  1 15:42 java-openjdk -> /etc/alternatives/java_sdk_openjdk
lrwxrwxrwx 1 root root   21 Jul  1 16:01 jre -> /etc/alternatives/jre
lrwxrwxrwx 1 root root   24 Jul  1 15:42 jre-11 -> /etc/alternatives/jre_11
lrwxrwxrwx 1 root root   32 Jul  1 15:42 jre-11-openjdk -> /etc/alternatives/jre_11_openjdk
lrwxrwxrwx 1 root root   40 Jul  1 15:42 jre-11-openjdk-11.0.7.10-4.el7_8.x86_64 -> java-11-openjdk-11.0.7.10-4.el7_8.x86_64
lrwxrwxrwx 1 root root   29 Jul  1 15:42 jre-openjdk -> /etc/alternatives/jre_openjdk

查看 Java 版本:

1
2
3
4
5
java -version

openjdk version "1.8.0_252"
OpenJDK Runtime Environment (build 1.8.0_252-b09)
OpenJDK 64-Bit Server VM (build 25.252-b09, mixed mode

4. 配置环境变量

编辑文件

1
vim /etc/profile

添加环境变量

1
2
export JAVA_HOME=/usr/lib/jvm/java-openjdk
export JRE_HOME=/usr/lib/jvm/jre-openjdk

使环境变量生效

1
source /etc/profile

5. 卸载 JDK

查看当前环境安装的 JDK :

1
2
3
4
5
6
7
8
9
rpm -aq | grep -i jdk

copy-jdk-configs-3.3-10.el7_5.noarch
java-1.8.0-openjdk-headless-1.8.0.252.b09-2.el7_8.x86_64
java-11-openjdk-headless-11.0.7.10-4.el7_8.x86_64
java-11-openjdk-devel-11.0.7.10-4.el7_8.x86_64
java-1.8.0-openjdk-1.8.0.252.b09-2.el7_8.x86_64
java-11-openjdk-11.0.7.10-4.el7_8.x86_64
java-1.8.0-openjdk-devel-1.8.0.252.b09-2.el7_8.x86_64

不需要一个一个删除,只需要删除 copy-jdk-configs 即可。

1
yum remove -y copy-jdk-configs-3.3-10.el7_5.noarch

Nginx 配置问题记录

1. server_name 无效

现象:Nginx 反向代理了两个应用,配置详情如下。发现访问 b.chenshaowen.com 和 a.chenshaowen.com 时,返回的都是 A 服务的请求。

 1
 2
 3
 4
 5
 6
 7
 8
 9
10
11
12
13
14
15
16
17
server {

	 listen 80;
	 server_name a.chenshaowen.com;
	 location / {
			proxy_pass http://A;
	 }
 }

server {

	listen 8080;
	server_name b.chenshaowen.com;
	location / {
		   proxy_pass http://B;
	}
}

原因:当所有 server 的规则都不匹配时,Nginx 会采用第一条 server 配置。

解决办法:在最前处,新增一条 server

1
2
3
4
5
6
server {
	  listen 80;
	  server_name XX.chenshaowen.com;
	  return 404;
 }
 # 其他 server

2. Nginx 增加密码验证

1.安装密码生成工具

1
yum install httpd-tools

2.生成账号密码

1
htpasswd -bc /your/password/file/path username password

3.Nginx 配置

1
2
3
4
5
location / {
	   auth_basic "input password";
	   auth_basic_user_file  /your/password/file/path;
	   ...
 }

4.重启 Nginx 服务

1
2
3
4
nginx -s reload
```

当再次访问时,Nginx 会弹出一个小框,提示输入密码。使用 username:password 即可登录、

Linux 网络流量监控终端工具 - nload

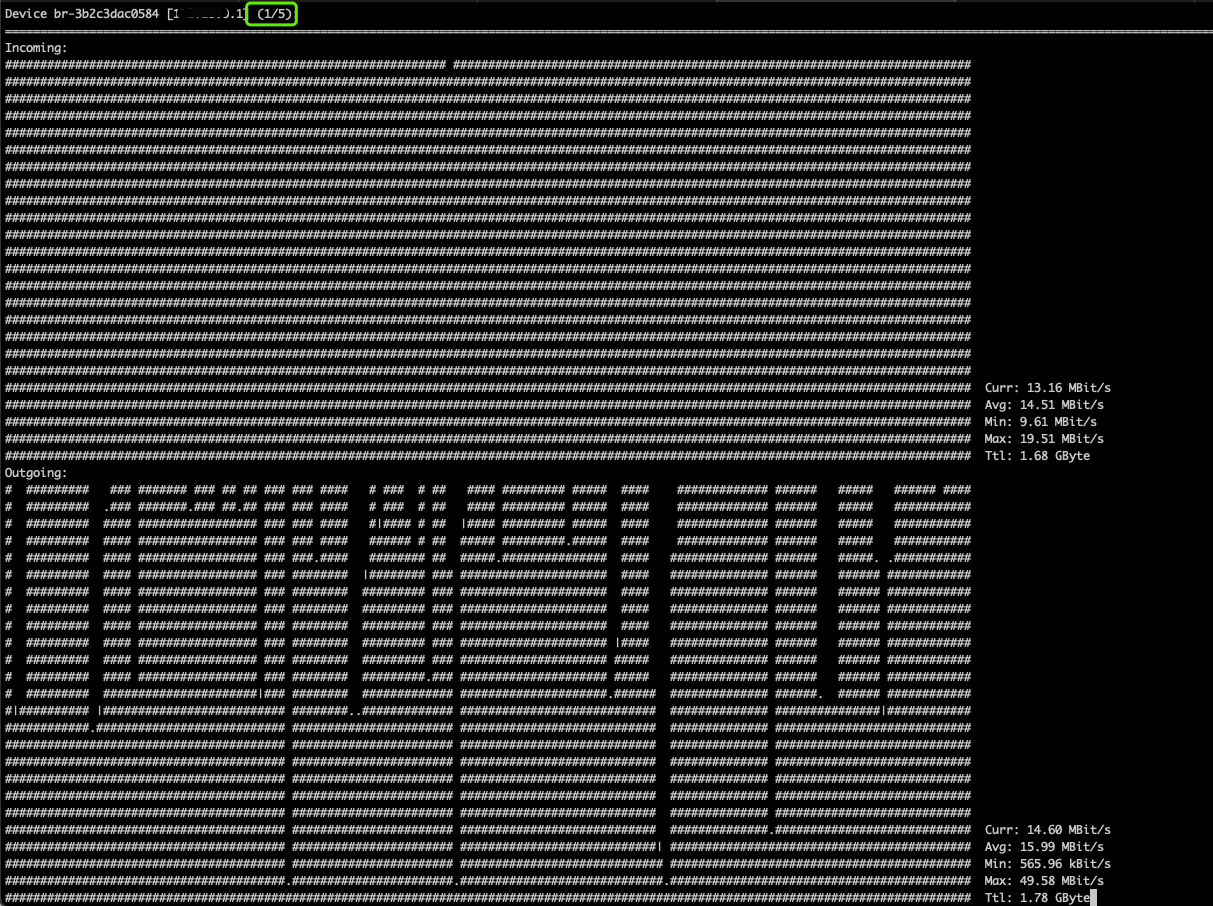
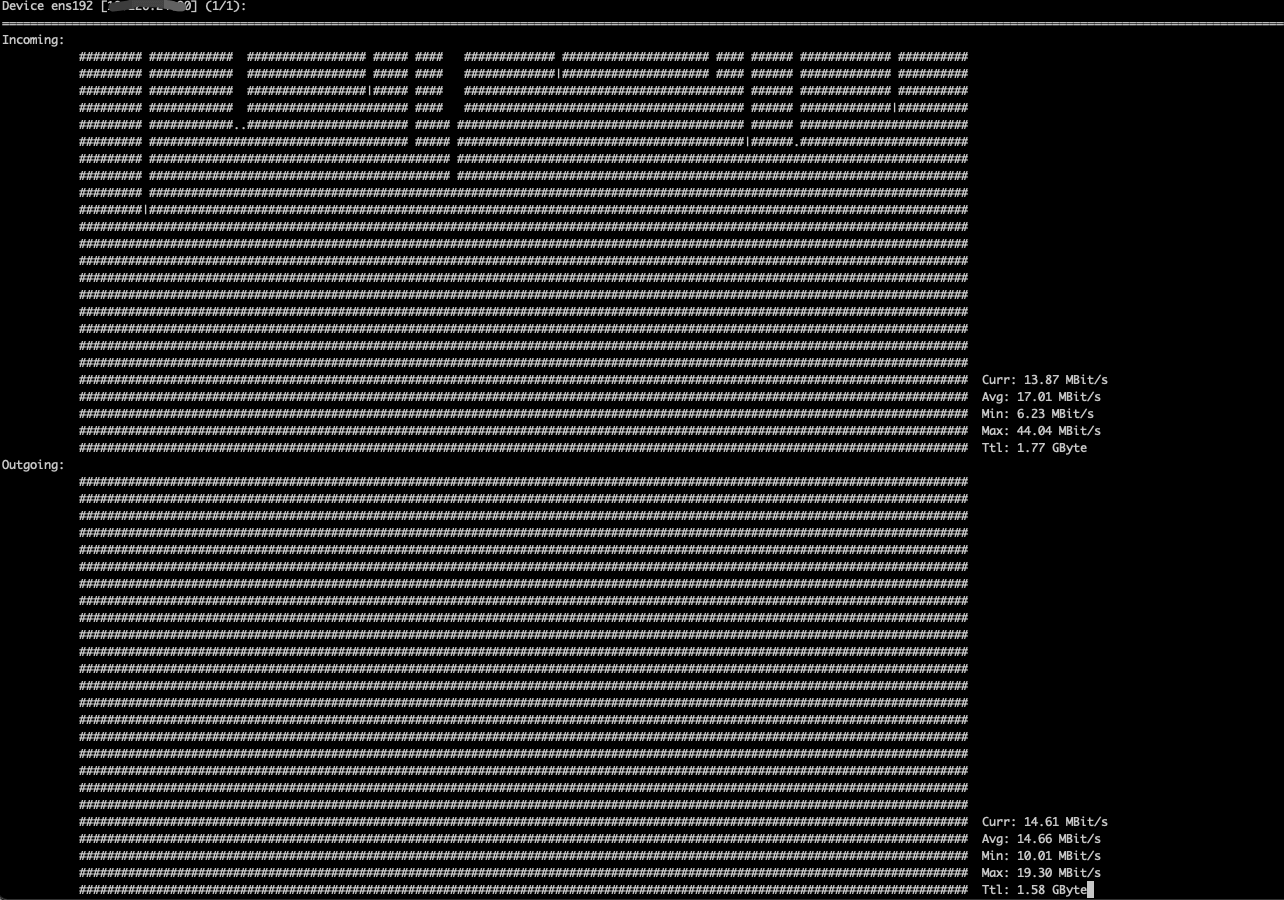
nload 是一个流量监控的终端工具,读取 /proc/net/dev 文件,绘制流量图。下面是一个简单的使用简介。

1. 安装

  • CentOS
1
yum install -y nload

如果系统的源找不到 nload 包,可以执行如下命令添加新源:

1
yum install -y https://dl.fedoraproject.org/pub/epel/epel-release-latest-7.noarch.rpm
  • Ubuntu
1
apt-get install -y nload

2. 参数

 1
 2
 3
 4
 5
 6
 7
 8
 9
10
11
12
13
14
15
16
17
18
19
20
21
nload --help

Command line syntax:
nload [options] [devices]
nload --help|-h

Options:
-a period       设置用于计算平均数的时间窗口的长度,默认值 30 秒
-i max_scaling  进入流量图显示的最大比例,默认值 10240
-m              显示多个设备,但是没有流量图。
-o max_scaling  出去流量图显示的最大比例,默认值 10240
-t interval     数据刷新的时间间隔,默认是 500 毫秒
-u h|b|k|m|g    设置流量的单位
   H|B|K|M|G    h: auto, b: Bit/s, k: kBit/s, m: MBit/s etc.
                H: auto, B: Byte/s, K: kByte/s, M: MByte/s etc.
                Default is h.
-U h|b|k|m|g    和 u 参数一样,但是显示的是总量 (没有 "/s").
   H|B|K|M|G    Default is H.
devices         检测的网络设备,默认检测全部设备

示例: nload -t 200 -i 1024 -o 128 -U M

3. 使用

1
nload

指定网卡

1
nload ens192

CentOS 7 下安装并配置 Zsh

1. 安装 zsh

1
sudo yum install -y zsh

2. 安装 oh-my-zsh

1
sh -c "$(curl -fsSL https://raw.github.com/ohmyzsh/ohmyzsh/master/tools/install.sh)"

建议将 Zsh 设置为默认的 Shell。

3. 安装插件

3.1 安装 autojump

1
sudo yum install -y epel-release
1
sudo yum install -y autojump-zsh

3.2 安装 zsh-autosuggestions

1
git clone git://github.com/zsh-users/zsh-autosuggestions $ZSH_CUSTOM/plugins/zsh-autosuggestions

3.3 安装 zsh-syntax-highlighting

1
git clone git://github.com/zsh-users/zsh-syntax-highlighting $ZSH_CUSTOM/plugins/zsh-syntax-highlighting

4. 添加 .zshrc 配置

1
sed -i 's/^plugins=(\(.*\)/plugins=(autojump zsh-autosuggestions zsh-syntax-highlighting \1/' ~/.zshrc

退出 Terminal, 再次登录即可。

网络性能测试工具 iperf

1. 安装

Ubuntu

1
apt-get install -y iperf3

CentOS

1
yum install -y iperf3

2. 参数

iperf3 的原理是通过客户端给服务端发送数据包来分析网络,有两种运行模式,客户端和服务端。

iperf3 的参数分为三部分,公共参数,客户端参数,服务端参数。

 1
 2
 3
 4
 5
 6
 7
 8
 9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
iperf3 -help

Server or Client:
  -p, --port      #         server port to listen on/connect to
  -f, --format    [kmgKMG]  format to report: Kbits, Mbits, KBytes, MBytes
  -i, --interval  #         seconds between periodic bandwidth reports
  -F, --file name           xmit/recv the specified file
  -A, --affinity n/n,m      set CPU affinity
  -B, --bind      <host>    bind to a specific interface
  -V, --verbose             more detailed output
  -J, --json                output in JSON format
  --logfile f               send output to a log file
  --forceflush              force flushing output at every interval
  -d, --debug               emit debugging output
  -v, --version             show version information and quit
  -h, --help                show this message and quit
Server specific:
  -s, --server              run in server mode
  -D, --daemon              run the server as a daemon
  -I, --pidfile file        write PID file
  -1, --one-off             handle one client connection then exit
Client specific:
  -c, --client    <host>    run in client mode, connecting to <host>
  -u, --udp                 use UDP rather than TCP
  -b, --bandwidth #[KMG][/#] target bandwidth in bits/sec (0 for unlimited)
                            (default 1 Mbit/sec for UDP, unlimited for TCP)
                            (optional slash and packet count for burst mode)
  --fq-rate #[KMG]          enable fair-queuing based socket pacing in
                            bits/sec (Linux only)
  -t, --time      #         time in seconds to transmit for (default 10 secs)
  -n, --bytes     #[KMG]    number of bytes to transmit (instead of -t)
  -k, --blockcount #[KMG]   number of blocks (packets) to transmit (instead of -t or -n)
  -l, --len       #[KMG]    length of buffer to read or write
                            (default 128 KB for TCP, dynamic or 1 for UDP)
  --cport         <port>    bind to a specific client port (TCP and UDP, default: ephemeral port)
  -P, --parallel  #         number of parallel client streams to run
  -R, --reverse             run in reverse mode (server sends, client receives)
  -w, --window    #[KMG]    set window size / socket buffer size
  -C, --congestion <algo>   set TCP congestion control algorithm (Linux and FreeBSD only)
  -M, --set-mss   #         set TCP/SCTP maximum segment size (MTU - 40 bytes)
  -N, --no-delay            set TCP/SCTP no delay, disabling Nagle's Algorithm
  -4, --version4            only use IPv4
  -6, --version6            only use IPv6
  -S, --tos N               set the IP 'type of service'
  -L, --flowlabel N         set the IPv6 flow label (only supported on Linux)
  -Z, --zerocopy            use a 'zero copy' method of sending data
  -O, --omit N              omit the first n seconds
  -T, --title str           prefix every output line with this string
  --get-server-output       get results from server
  --udp-counters-64bit      use 64-bit counters in UDP test packets

3. 测试

  • 服务端
1
iperf3 -s -i 1 -p 30000
  • 客户端

测试 TCP

 1
 2
 3
 4
 5
 6
 7
 8
 9
10
11
12
iperf3 -c 1.2.3.4 -p 30000 -i 1

Connecting to host 1.2.3.4, port 30000
[  4] local 2.3.4.5 port 44794 connected to 1.2.3.4 port 30000
[ ID] Interval           Transfer     Bandwidth       Retr  Cwnd
[  4]   0.00-1.00   sec   911 MBytes  7.64 Gbits/sec   98   1.21 MBytes       
...
[  4]   9.00-10.00  sec   910 MBytes  7.63 Gbits/sec   13   1.16 MBytes       
- - - - - - - - - - - - - - - - - - - - - - - - -
[ ID] Interval           Transfer     Bandwidth       Retr
[  4]   0.00-10.00  sec  9.18 GBytes  7.88 Gbits/sec  231             sender
[  4]   0.00-10.00  sec  9.17 GBytes  7.88 Gbits/sec                  receiver

测试 UDP,包大小 1460 bit

 1
 2
 3
 4
 5
 6
 7
 8
 9
10
11
12
iperf3 -c 1.2.3.4 -p 30000 -i 1 -u -l 1460

Connecting to host 1.2.3.4, port 30000
[  4] local 2.3.4.5 port 57562 connected to 1.2.3.4 port 30000
[ ID] Interval           Transfer     Bandwidth       Total Datagrams
[  4]   0.00-1.00   sec   116 KBytes   946 Kbits/sec  1183  
...
[  4]   9.00-10.00  sec   128 KBytes  1.05 Mbits/sec  1310  
- - - - - - - - - - - - - - - - - - - - - - - - -
[ ID] Interval           Transfer     Bandwidth       Jitter    Lost/Total Datagrams
[  4]   0.00-10.00  sec  1.24 MBytes  1.04 Mbits/sec  0.012 ms  33/12979 (0.25%)  
[  4] Sent 12979 datagrams

常用的一些 MYSQL 命令

1. 免密登录

  1. 修改 /etc/my.cnf,在 [mysqld] 中添加一行:
skip-grant-tables=1
  1. 重启 mysqld 服务
1
systemctl restart mysqld
  1. 使用 root 用户登录到 MySQL
1
mysql -u root

2. 允许全部访问来源

  1. 登录 MySQL
1
mysql -u root -p

在 mysql 交互命令行中输入:

1
2
3
4
USE mysql;
SELECT user, host FROM user;
update user set host = '%' where user = 'root';
FLUSH PRIVILEGES;

3. 导出全部数据

1
mysqldump -uroot -proot --all-databases >/tmp/all.sql

进阶的 curl 用法

1. Restful 请求

1
curl -X POST --data 'keyword=value' http://domain.com/mypath/

-X 后面还可以是 DELETE PUT 等。

2. 添加头部

1
curl -H 'Content-Type:application/json' -H 'Authorization: bearer MyToken' http://domain.com/mypath/

3. Basic 验证访问

1
curl -u username:password http://domain.com/mypath/

4. 下载并执行

1
curl -sSL http://domain.com/my.sh | bash

5. 忽略证书校验

1
curl -k https://domain.com/mypath/

6. 设置代理

1
curl -x socks5://proxyuser:proxypassword@proxy.domain.com:8001 https://domain.com/mypath/

7. 指定 Host 使用 IP 访问

1
curl -H 'Host: www.domain.com' 1.2.3.4:8000

陈少文
作者
陈少文